State crosses contexts.
Ask whether scope and provenance travel with it.
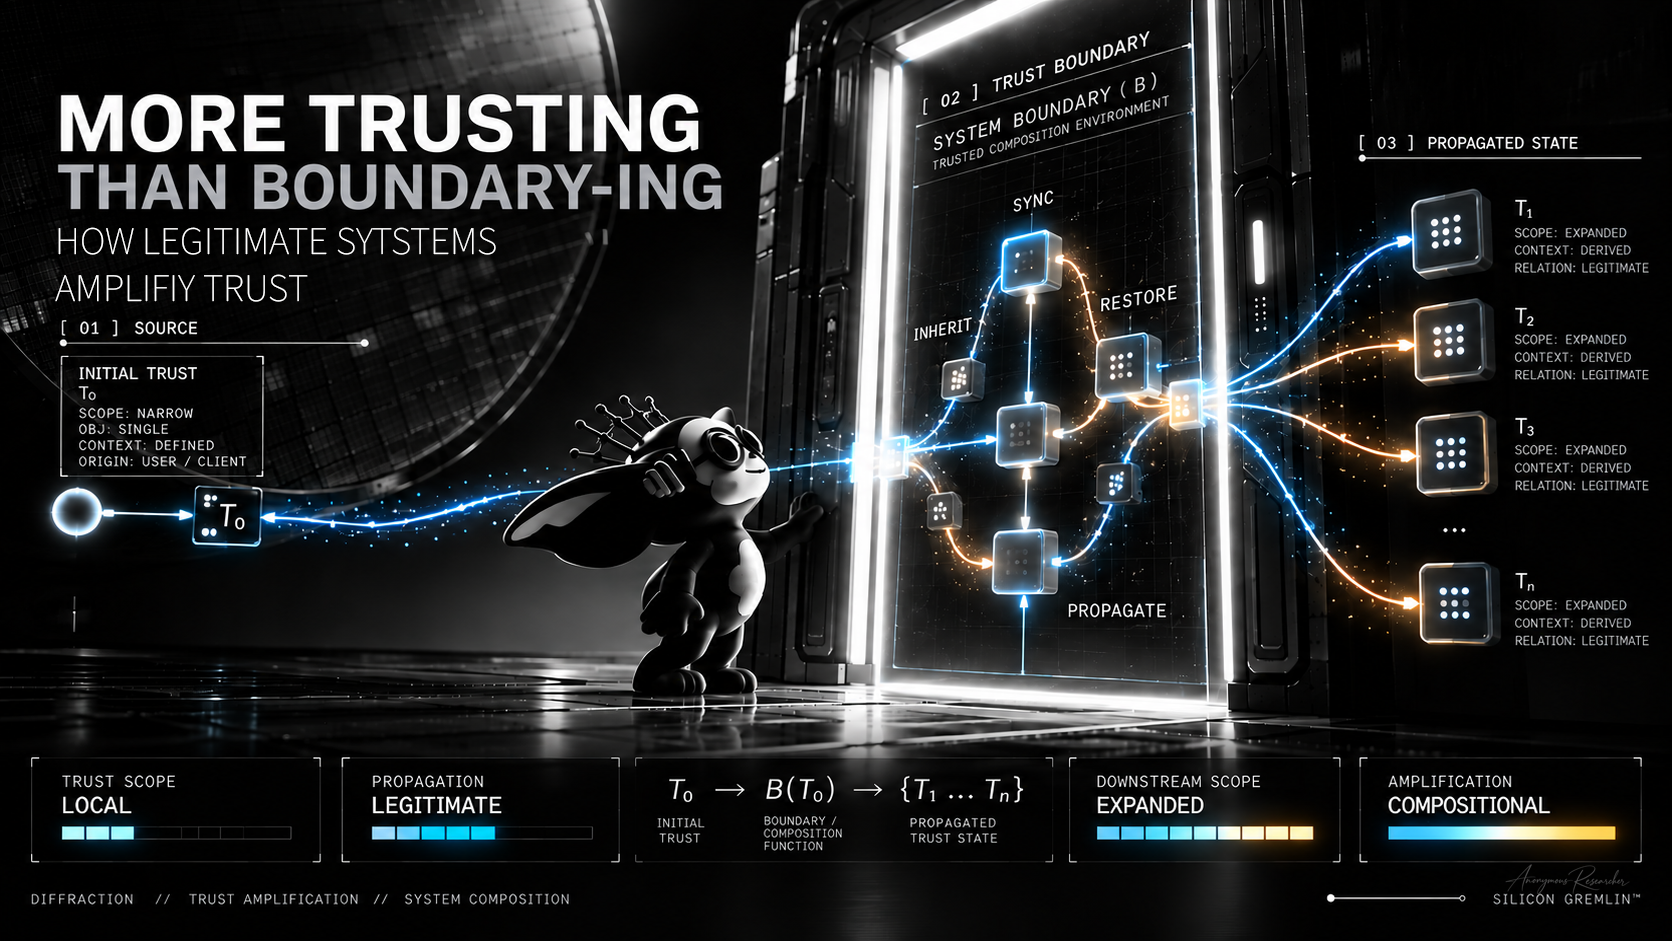
Silicon Gremlin · Kimbrow Consulting LLC · Blog
How legitimate systems amplify trust
The boundary did not fail. That is the problem I am interested in.
THE BOUNDARY WORKED
Security language is comfortable around violations. A boundary rejects an operation, an identity exceeds its authority, an object becomes reachable from a context that should not reach it. Those failures are useful because the direction of the mistake is obvious.
The harder case is when the operation is allowed.
A state synchronizes. An identity is accepted. A cache is reused. A workload is scheduled. A snapshot is restored. A downstream component consumes state produced somewhere else. Every transition can be legitimate in isolation, and the boundary can behave exactly as designed.
A system does not need to cross a boundary incorrectly for the meaning of trust to change on the other side.
That is the class of behavior I want to model: not the obvious bypass, but the relationship created when individually reasonable transitions compose into a larger system.
TRUST HAS SCOPE
Calling a relationship trusted or untrusted compresses away the part I care about. A useful trust state has context: who established it, what object it concerns, which operations it permits, where it is valid, how long it persists, and what assumptions downstream systems are allowed to inherit from it.
If that state moves, preserving the bytes is not necessarily the same thing as preserving the meaning. A restored object can be identical while its environment is different. A synchronized state can be legitimate while its downstream reach is larger. A derived identity can be valid while carrying assumptions that were only justified in the originating context.
THE TRUST AMPLIFIER
This is where the trust-amplifier idea from DIFFRACTION becomes useful. Start with a state whose authority is narrow and defined. Pass it through a system boundary that can synchronize, inherit, restore, derive, or propagate state. The output is no longer necessarily one object in one context.
The expression does not say that B is malicious, defective, or bypassed. It says that B is compositional. The system takes one meaningful relationship and participates in producing several downstream relationships.
Amplification is therefore not synonymous with vulnerability. It is a property worth measuring. The security question begins when the effective reach, persistence, or interpretation of the derived states exceeds what the original trust decision was intended to justify.
TRUST CONSERVATION
Shared systems are very good at preserving state. They have to be. Synchronization that forgets objects, recovery that cannot reconstruct them, and schedulers that cannot preserve execution assumptions are not useful systems.
But security depends on more than continuity of state. It depends on continuity of justification.
This is the conservation question: when a legitimate transformation produces a downstream state, which properties must remain invariant for the resulting trust relationship to mean the same thing?
If provenance disappears, scope broadens, revocation stops propagating, or a downstream consumer interprets the state under stronger assumptions, then the system may have preserved the artifact while changing the authority represented by it.
MORE TRUSTING THAN BOUNDARY-ING
We often draw the boundary where an operation is admitted or rejected. That remains necessary. It may simply be too small a surface for systems whose useful behavior depends on composition.
Ask whether scope and provenance travel with it.
Ask which assumptions downstream consumers receive.
Ask whether the original authority is still valid here.
Ask which relationships the substrate can create or preserve.
Ask whether derived authority is narrower, equal, or broader.
Ask whether every propagated relationship learns that it ended.
The point is not that shared infrastructure is inherently unsafe. The point is that the boundary has to account for the behavior that makes sharing useful. Otherwise we may be measuring whether the door worked while ignoring what the building legitimately carries between rooms.
THE QUESTION AFTER THE BOUNDARY
Nor should it. The ability to compose resources is one of the reasons modern systems scale, recover, synchronize, and remain economically usable. The useful question is not how to abolish sharing. It is whether our models of isolation describe enough of what sharing actually does.
A boundary can correctly prevent an unauthorized transition. It cannot, by itself, guarantee that an authorized trust relationship remains the same thing after synchronization, inheritance, restoration, derivation, or reuse across shared substrate.
So I am less interested in asking whether the boundary exists than in asking what the system permits trust to become after crossing it.
The boundary did not fail.
Perhaps we have been asking too little of the boundary.